Learning
PwC Confirms Learning Records Breached in Third-Party Vendor Attack
PwC confirmed a breach of a third-party vendor site used for employee learning records and is investigating claims by Everest ransomware that it stole 590 gigabytes of employee data. PwC said the incident did not affect its network or operations, and the site does not house client data, sensitive personal data, or financial information. Everest ransomware, active since late 2020, has previously operated as an initial access broker and targeted critical-infrastructure providers.
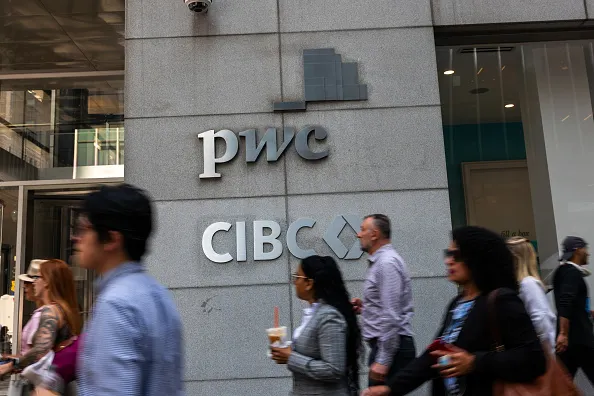
PwC on Monday said it was investigating claims that hackers had breached a third-party vendor site the company uses to house employee learning records.
The company disclosed the breach amid claims from Everest ransomware that it had stolen 590 gigabytes of employee data in an attack.
PwC has not commented on the specific ransomware claim. However, after learning of the incident, the company “acted promptly to secure the environment” and conducted a thorough review, according to a PwC Global spokesperson.
The company said the breach did not affect its network or any of its operations. The site does not house any “client data, sensitive personal data or financial information,” according to the spokesperson.
PwC, based in London, is one of the world’s largest professional services firms and has more than 364,000 workers worldwide.
Everest ransomware recently targeted critical-infrastructure providers across the globe. Since emerging in late 2020, the group has operated as an initial access broker and provided credentials to other groups, according to research provided by Halcyon.
The group also recruited insiders to work with them, offering cash payments and profit sharing. The group claimed attacks against multiple international airports in 2025, through an attack targeting Collins Aerospace.